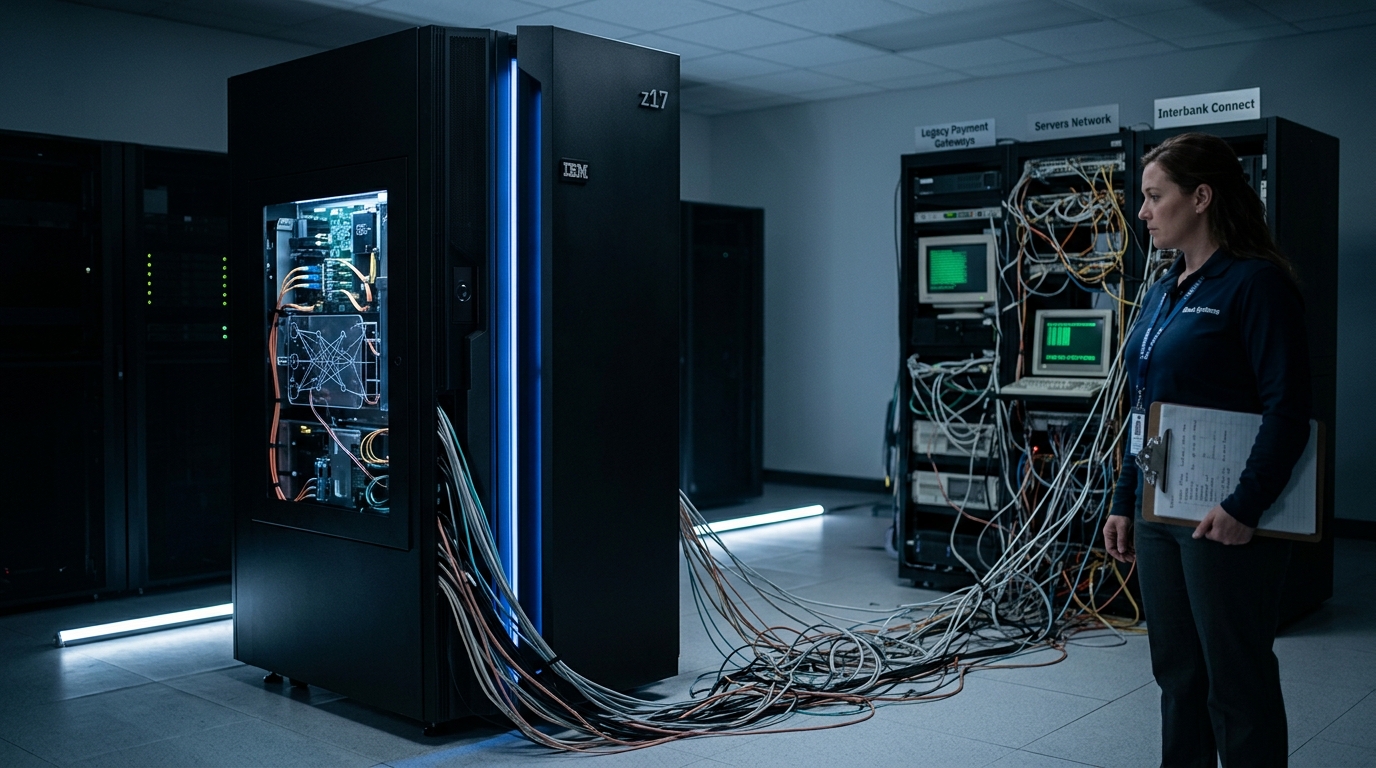
IBM has already done the hard part. The z17 mainframe is quantum-safe ready, with IBM implementing quantum-safe cryptography that utilizes algorithms like CRYSTALS-Kyber and CRYSTALS-Dilithium, both selected by NIST for standardization. IBM uses both classical and quantum-resistant algorithms during secure boot to verify that system firmware is authentic and IBM-approved, relying on a dual-signature scheme anchored in the IBM Z Root of Trust. That is firmware-level protection, not a software patch applied after the fact.
The gap is not in the hardware. It is everything connected to it.
Distributed estates rely on complex chains of vendors, products, HSMs, API gateways, and cloud services. IBM has described quantum-safe migration on IBM Z as a full-stack challenge that extends beyond the mainframe itself. That bottleneck matters more than the mainframe spec sheet, because IBM has long said IBM Z can process about 12 billion encrypted transactions a day. Every one of those transactions eventually touches something outside the box.
DigiCert’s July 2026 survey of 1,001 enterprise security leaders found 87% of organizations are planning, testing, or implementing post-quantum cryptography, but only 7% have deployed quantum-safe or hybrid cryptography across most of their digital certificates. That figure is up from just 5% in DigiCert’s first annual survey, a gap DigiCert framed as a planning-to-deployment disconnect.
F5 Labs found that only about 3% of banking websites support post-quantum cryptographic capabilities. That figure captures the distance between what IBM has embedded in its infrastructure and what the broader banking perimeter actually looks like today.
Regulators are starting to use examination authority to close that distance. In the U.S., federal banking regulators have been signaling that quantum risk and crypto-agility fall under core expectations for operational resilience and third-party risk management, even as agencies have not published a single OCC examination start date specifically labeled as a post-quantum requirement. A July 2026 whitepaper on quantum preparedness of Hong Kong’s banking sector, supported by the HKMA, found the sector is still early in readiness and that third-party and vendor dependencies are a major friction point for PQC transition.
Regulatory pressure on third-party dependencies is not limited to quantum risk. European supervisors are already running live oversight of banks’ critical ICT third-party providers under DORA, with penalty authority attached.
The threat driving that urgency is not theoretical. In the financial industry, the “Harvest Now, Decrypt Later” approach, where attackers steal encrypted data today for future quantum decryption, is already demanding action. A bank communication encrypted under RSA-2048 and intercepted today could become readable once a cryptographically relevant quantum computer exists, regardless of what the bank does between now and then.
IBM’s commercial position here is straightforward. The IBM Quantum Safe platform includes the Quantum Safe Explorer for cryptographic inventory and discovery, and IBM z16 and later ship with hardware-backed quantum-safe mechanisms used in secure boot and cryptographic infrastructure. The firm sells the problem’s solution and the tools to assess the problem’s scope. That is a defensible position as long as the examination cycle and the harvest-now threat continue to accelerate enterprise urgency. The mainframe may be ready. The question examiners will be asking is whether the payment rails around it are.